Stop the request
before it reaches
your application.
Path rules, rate limits, signature filtering, velocity gates, country blocking, multi-tenant, one-size-fits-all licensing and more running on your infrastructure. No proxy in front of your traffic. Your request and log data never leaves your host.
Watch every request as it happens.
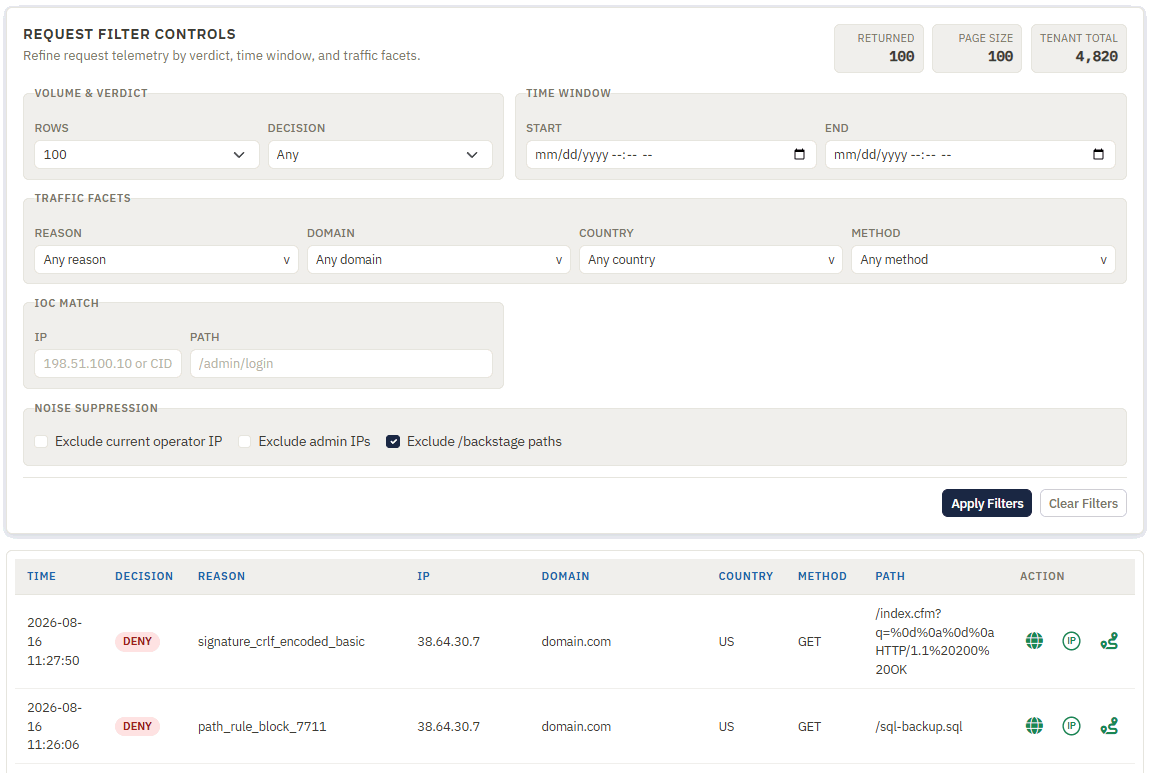
Every request that hits your host is evaluated and logged in real time — allowed, denied, or rate-limited — with the site, IP, path, and matching rule laid out plainly. Nothing is sampled or delayed; what the panel shows is what just happened on your server.
- Allow, deny, and rate-limit decisions logged with the matching rule
- Live counts for requests/min and blocked today
- Nothing sampled — every request your host receives is recorded
IP, path, user-agent, signature, and rate-limit — all in one editor.
Rules are stored per site and evaluated in a fixed order, first match wins. Add an IP range, block a WordPress probe path, or write a signature regex without leaving the admin panel — changes take effect on the next request, no redeploy.
- First match wins, evaluated in a fixed, predictable order
- Changes take effect on the next request — no redeploy
- Scoped per site, so one ruleset never leaks into another
Repeat offenders get jailed automatically.
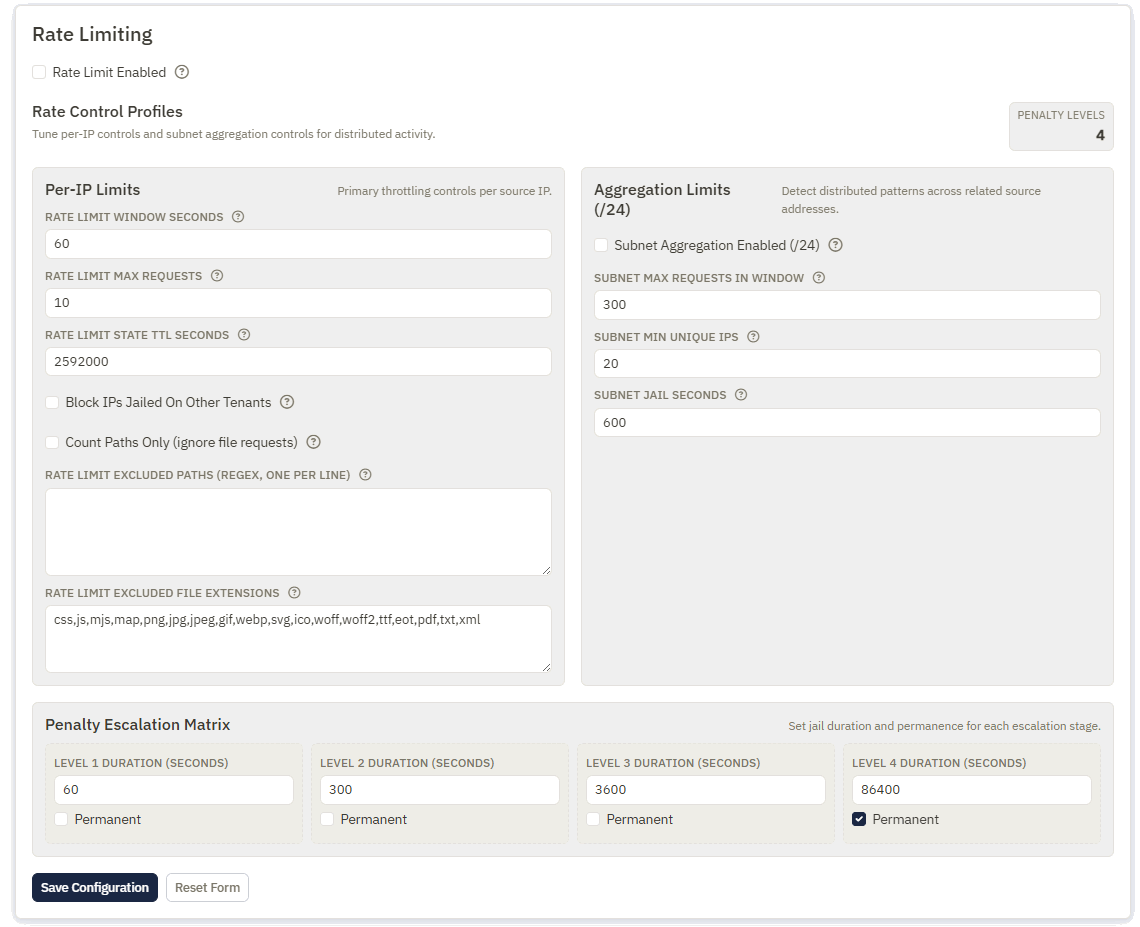
A rolling-window counter tracks request bursts per IP. Cross the threshold and the address is jailed for a configurable window — no manual intervention required, though an operator with the right permission can release early.
- Rolling-window counter tracks bursts per IP
- Jailed addresses are logged with the rule that triggered it
- Operators with permission can release early
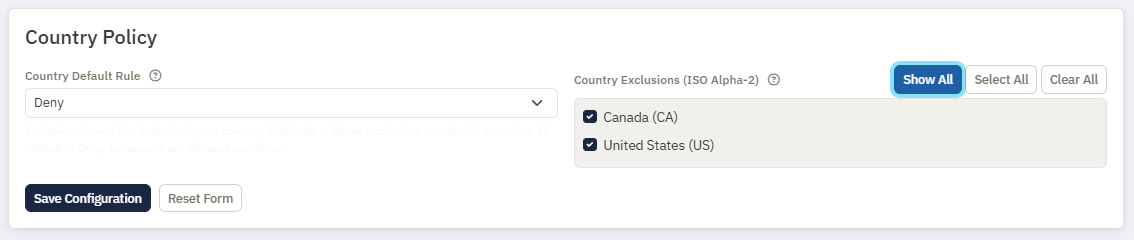
Every request is attributed a country before it's evaluated.
Ignite WAF resolves each request's IP to a country via a bundled MaxMind GeoIP2 database, with REST fallback for the rare miss — no outbound call required for the common case. Use that attribution to allow, deny, or simply watch traffic by country.
- Bundled MaxMind GeoIP2 database — no outbound call for the common case
- REST fallback for the rare miss
- Allow, deny, or simply watch traffic by country
Grade your live Content-Security-Policy header, A through F.
Fetches your site's live CSP header and grades it across 40+ directive checks — run it on demand or on a schedule, with results emailed to your team so drift gets caught before it matters.
- 40+ directive checks against your live header
- Run on demand or on a schedule
- Results emailed to your team
TLS, cookies, CORS, and clickjacking — checked together.
Quick Scan runs a wider sweep beyond CSP: TLS configuration, cookie flags, CORS policy, clickjacking protection, and exposed paths, graded the same A–F way so results are easy to compare over time.
- TLS configuration and certificate chain
- Cookie flags, CORS policy, exposed paths
- Same A–F grading, easy to compare over time
Run your whole client roster from one panel.
Each site gets its own scoped rules, logs, and reports. Agencies and platform teams manage a full roster of client sites from a single lightweight admin panel instead of standing up a separate install per client.
- Each site gets its own scoped rules, logs, and reports
- One admin panel, no per-client install
- Built for agencies and platform teams
Give operators exactly the access they need, nothing more.
Logs, config, users, sites, and reports can each be scoped independently per operator, per site. A junior operator can be limited to viewing logs on one client's site while a lead keeps full access across the roster.
- Logs, config, users, sites, and reports scoped independently
- Per-site, not just per-role
- A junior operator can be limited to one client's logs
Try Ignite WAF in your own environment.
Create an account and get a 14-day trial — no card required. $399/year per server or VM after that.